01
AI-generated code
More machine-written code, more inherited patterns and semantic risk. AI coding assistants accelerate delivery but multiply the attack surface faster than traditional AppSec tools can keep up.
CyberSagacity validates findings from application security tools, identifies testing coverage gaps, and prioritizes vulnerabilities by likelihood, business impact, and financial exposure—across human-written, open-source, and AI-generated code.
Give development, security, and business teams—and the AI agents and workflows they use—clear direction on what to fix first and why. Focus engineering effort where it reduces the most risk, and measure the results in business terms.
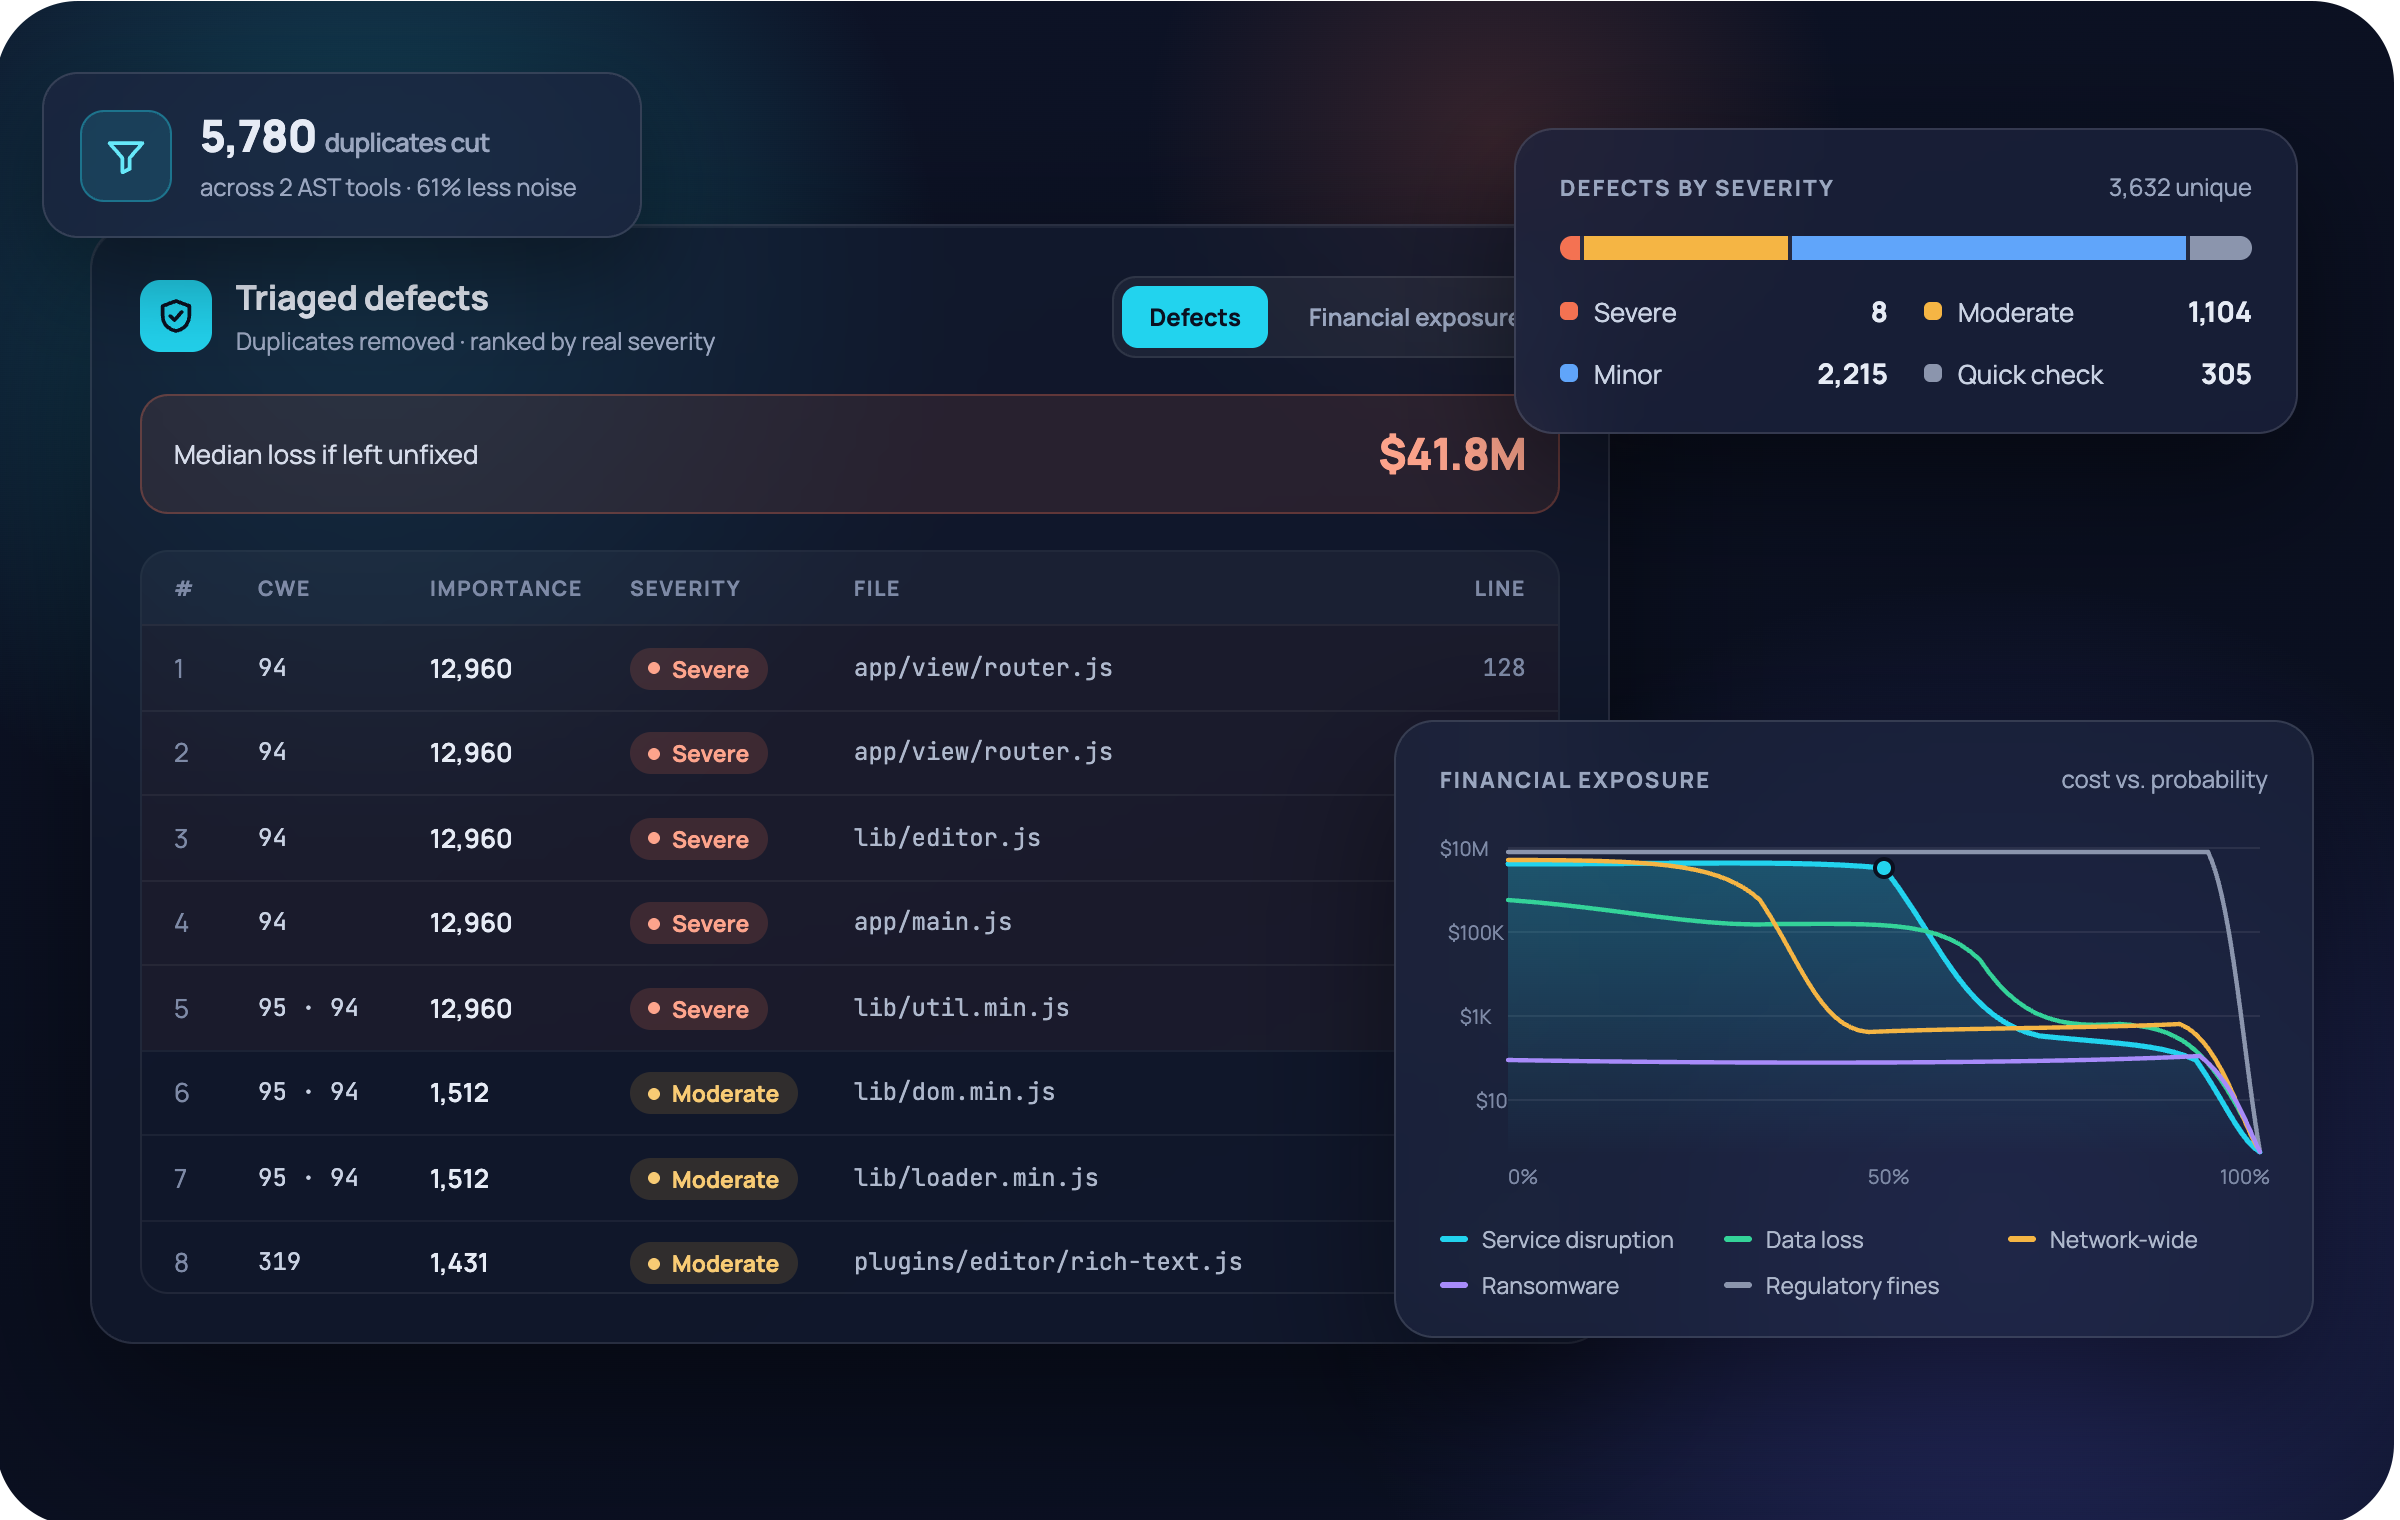
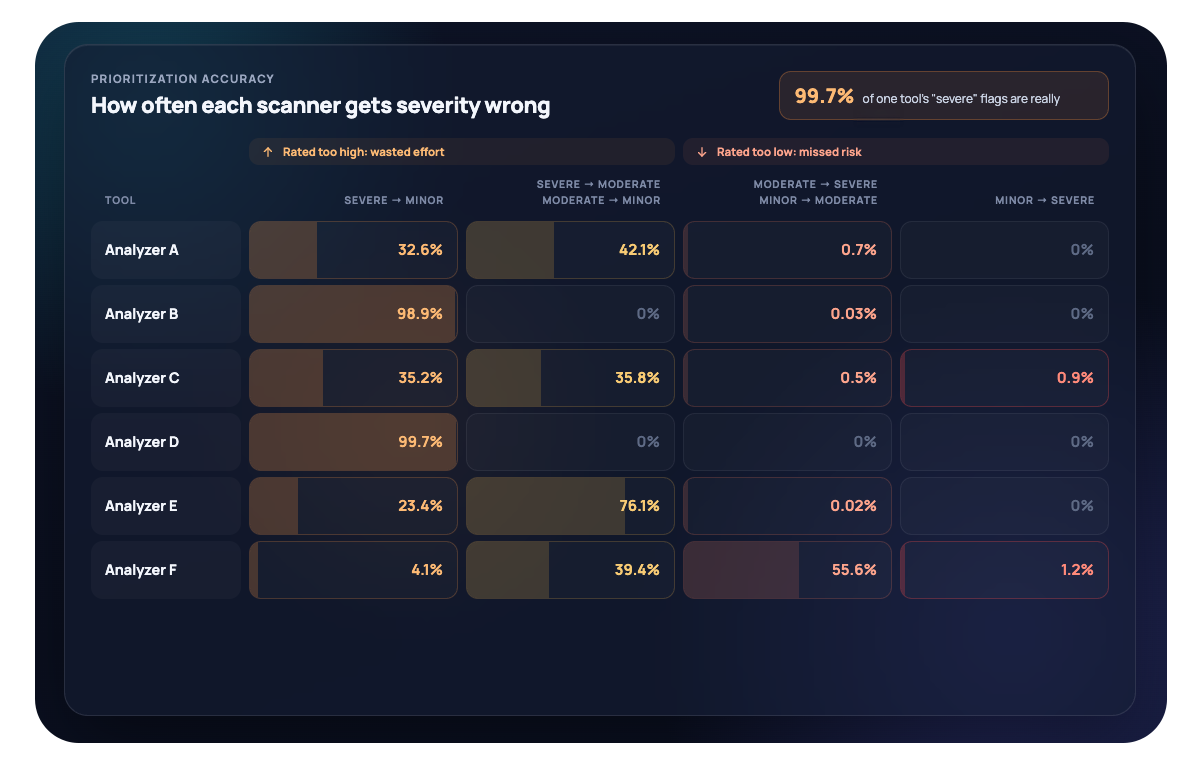
Application security tools and AI agents can produce conflicting, duplicate, or inaccurate findings—wasting remediation effort and obscuring real risk.
CyberSagacity produces validated, risk-ranked application security intelligence so teams, AI agents, and automated workflows know what to fix first—and why.
They produce false positives and miss meaningful defects. They disagree on severity across tools. They fail to connect findings to business, compliance, and financial exposure.
ASPM and ASOC platforms aggregate findings and add workflow visibility, but aggregation does not correct inaccurate source data. Bad data just becomes easier to see.
Source: CyberSagacity AST study — 57 AST tools, 19 languages, 67K+ rules, 497 CWEs, 35M+ curated defects. Read the study →
Open-source dependencies, cloud-native systems, and AI-generated code expand what teams must secure. More findings don’t make priorities clearer.
CyberSagacity produces application security intelligence that validates findings, ranks remediation priorities, and quantifies financial risk exposure—giving teams, AI agents, and automated workflows clear direction on what to fix first, with evidence to explain why.
More machine-written code, more inherited patterns and semantic risk. AI coding assistants accelerate delivery but multiply the attack surface faster than traditional AppSec tools can keep up.
Expanding dependency trees widen the exploitable surface. Every transitive dependency is a potential entry point — and most scanners miss the ones that matter.
Enterprises still own application-layer defects. Cloud providers secure the infrastructure, but the code your teams ship is your responsibility — and it is more distributed than ever.
Regulators, insurers, and boards require quantified evidence. Severity labels and alert counts no longer satisfy compliance or due-diligence requirements.
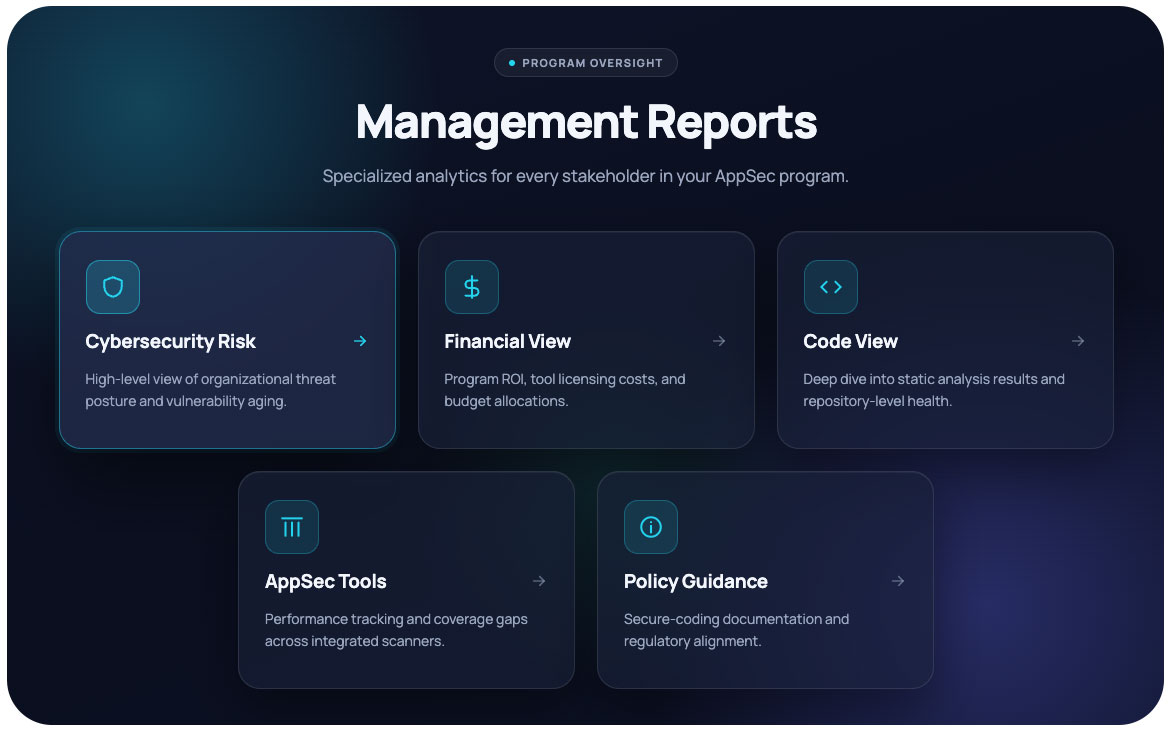
CyberSagacity validates security findings, identifies coverage gaps, and prioritizes remediation by business impact across your software portfolio, however the code is created or sourced—helping teams reduce remediation time and cost while lowering application risk. A common set of risk, productivity, and ROI metrics helps security, engineering, and leadership measure and monitor AppSec outcomes.
Our documented use cases report 5×–100× productivity gains and 3×–10× improvements in AppSec ROI.
SATraits assesses application security testing coverage and application risk. SATriage validates defect and vulnerability findings, prioritizes remediation, and quantifies financial risk exposure.
Together, they give development, security, and business teams a common language for application risk—and provide teams, AI agents, and automated workflows clear priorities on what to fix first and why.
Evaluates the effectiveness, coverage, overlap, and accuracy of your AST tools. Exposes false negatives and blind spots.
Converts raw defect data into ranked, business-aligned remediation intelligence. Quantifies financial exposure.
CyberSagacity products ingest defect and vulnerability findings from security tools, AI, and other sources. They validate and correct findings, add business and compliance context, prioritize remediation by exploitability and potential consequences, and quantify financial risk exposure.
The result is application security intelligence that tells teams, AI agents, and automated workflows what to fix first—and why.
AST and AI-AppSec sources.
Normalize identities, metadata, and classifications.
Correlate defects to assets, controls, and business context.
Exploitability + impact + compliance + dollars.
Audit- and executive-ready evidence.
CyberSagacity prioritizes every defect using four complementary approaches — statistical risk, financial loss and ROI, mission-critical consequence and attack risk, or any combination — so decisions rest on technical, operational, and financial risk, not a severity label.
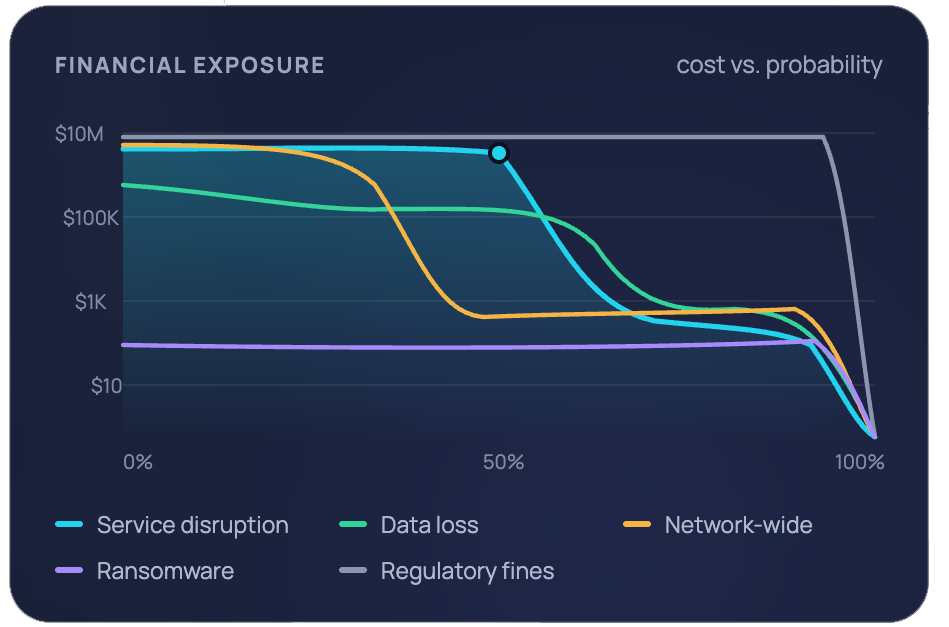
Cyber-risk quantification, financial-loss modeling, and audit-ready evidence.
Validated, correlated findings across every tool, with coverage and false-negative intelligence.
A ranked, deduplicated list of what actually needs fixing, delivered inside your tools and IDE.
Decision context through MCP, open APIs, and policy guardrails.
Every finding is statistically corrected and confirmed before it is prioritized or reported.
Defects are ranked 1-to-N by exploitability, consequence, and compliance impact.
Exposure, expected loss, remediation ROI, and residual risk in the language boards and CFOs use.
AST tools find defects. ASPM and ASOC tools aggregate findings. CyberSagacity determines what is true, what matters, what it costs, and what to do next.
| AST / AI discovery | ASPM / ASOC | CyberSagacity | |
|---|---|---|---|
| Signal quality | Raw findings | Aggregated findings | Validated ground truth |
| Prioritization | Severity labels | Routing rules | Exploitability + impact + ROI |
| Proof to exec / audit | Alert counts | Dashboards | Evidence-grade reports |
| Tool overlap / gaps | Unknown | Partially visible | Quantified and validated |
Deploy as SaaS, private cloud, hybrid, or on-premises — including secure environments.
30 years of AppSec research; patented defect intelligence.
Enterprise software leader; global scaling and partnerships.
Cybersecurity GTM, exits, partnerships, and capital formation.
Enterprise and government partnership development.
Cloud-native platform, AI product, DevSecOps, SaaS delivery.
Chris Near's Black Hat research on AST accuracy and coverage.
Read the study →
An executive guide to AST, ASPM, ASOC, and what actually reduces risk.
Download →
Perspectives on turning AppSec findings into decision-grade intelligence.
Subscribe on LinkedIn →